Documentation sections
Flow setup
Step 2. Filtering
Whom to let through to the offer. In “Tracker” mode the step is called “Traffic assessment”: the filter doesn't cut anyone, it only flags bots, and the report shows how much of the paid traffic was bots.
On this page
Check strictness

- Default
- “Another source + Balanced”
- Recommended
- “Balanced”; “Strict” when the platform sends a lot of bots — check how many real people you lose in Flow diagnostics
- Plan
- all plans; the IP limit and warm-up on Professional and up, and on the trial; on Starter they are reset to zero
- Common mistake
- going straight to “Strict” — some real people get cut: “IPv6 traffic blocked” (
IPV6_BLOCKED), “JavaScript required” (JS_REQUIRED), “Too many clicks from one IP” (CLICKS_PER_IP_LIMIT); and those who leave the waiting page before the minimum time don't get into the log at all
| Soft | Balanced | Strict | |
|---|---|---|---|
| IP blacklists, headless browsers | yes | yes | yes |
| VPN and proxies, datacenter ASNs | — | yes | yes |
| Clicks per IP limit | — | per platform | per platform, 2 at most |
| IPv6, required JS, live interaction | — | — | yes |
| Minimum time on page | — | — | 1500 ms |
For most campaigns we recommend “Balanced”. “Strict” also cuts some real people: choose it when the platform sends a lot of bots, and check the loss in Diagnostics.
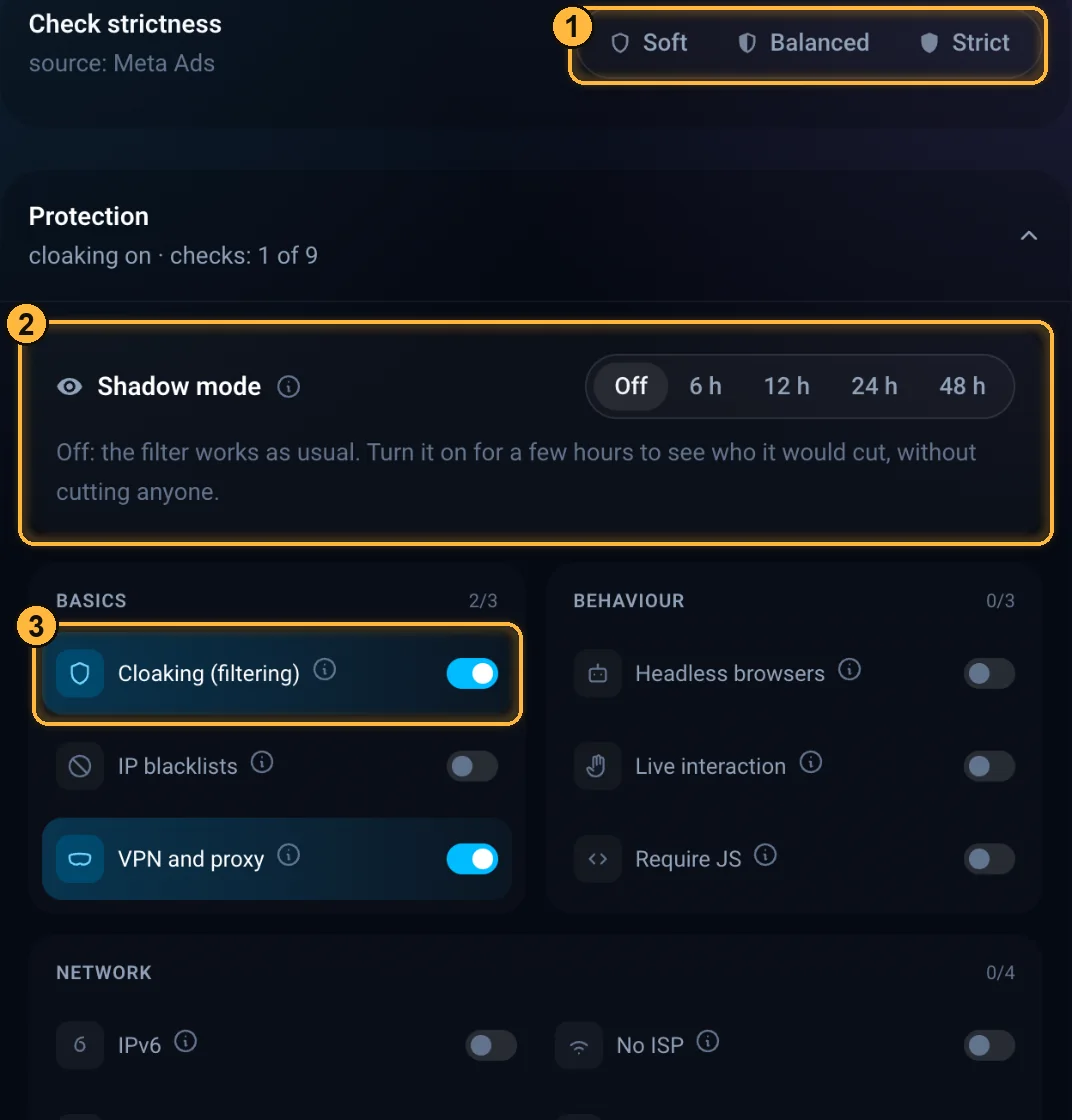
The Soft / Balanced / Strict switch. Under the heading you can see which platform the protection is tuned for: “source: …”, “platform: …” or “no source chosen — profile not applied”. Under the switch is a hint for the selected level, and what ends up turned on is shown in the header of the “Protection” block: “cloaking on · checks: N of 9”.
| Level | What it cuts |
|---|---|
| Soft | Clearly untargeted traffic: addresses from IP blacklists and bots. The risk of losing real people is minimal, and there are no IP limits. |
| Balanced | Plus VPN, proxies and datacenters, and a daily clicks per IP limit. Suits most campaigns. |
| Strict | Plus IPv6 blocking, a required JS check, a minimum time on page and a tight IP limit. May cut some of your target traffic. |
The platform comes from the source on step 1. Each platform has preset values:
| Platform | No ISP | Warm-up | Require JS | Clicks per IP (Balanced) | Why |
|---|---|---|---|---|---|
| Facebook Ads | on | 50 | no | 3 | Facebook's in-app browser often drops the referrer, so the referrer check is off. The first moderation checks go to the White Page. |
| Google Ads | on | 30 | yes | 2 | Google passes a click tag (gclid), so JS can be required. |
| TikTok Ads | off | 50 | no | 3 | Blocking visits with no ISP is off. |
| Native and push | on | 100 | yes | 5 | More clicks per IP and a long warm-up. |
| Another source | on | 0 | yes | 3 | Standard checks without platform-specific rules. |
What the strictness level changes:
| Level | VPN and proxies | Datacenter ASNs | Live interaction | IPv6 | Min. time | Require JS | Clicks per IP per day |
|---|---|---|---|---|---|---|---|
| Soft | off | off | off | off | 0 | per platform | no limit |
| Balanced | on | on | off | off | 0 | per platform | per platform |
| Strict | on | on | on | on | 1500 ms | always | 2 |
- At every level, cloaking, IP blacklist blocking and headless browser blocking (browsers driven by a program) are on, and the referrer check is off.
- A new flow starts with “Another source + Balanced”.
- Features your plan doesn't include are switched off after applying: for example, on Starter the clicks per IP limit and warm-up are reset to zero.
- If you've already changed the toggles by hand, changing the strictness or source brings up a “Replace your protection settings?” window with a “before → after” list. Apply replaces the settings. Keep mine changes only the selected level or source and keeps your toggles as they are. If nothing changes or the form hasn't been touched yet, there's no window.
How the decision is made
Some checks cut a visit right away (IP blacklists, an obvious headless browser, an audience rule). The rest add up to a trust score: every suspicious signal adds a penalty, and if the total goes over the threshold, the visitor sees the White Page. The protection toggles decide how much each signal weighs.
Protection
- Default
- as in “Another source + Balanced”: cloaking, IP blacklists, VPN and proxies, data center ASNs, headless browsers, required JS and “without ISP” (from Professional) on; IPv6, live interaction, “without referrer” and shadow mode off
- Recommended
- for a new campaign, shadow mode for 24 hours: diagnostics show whom the filter would cut while real people go to the offer
- Plan
- all plans; “without ISP” and “without referrer” from Professional
- Common mistake
- switching cloaking off — everyone sees the White Page: “Cloaking switched off” (
CLOAK_OFF); turning on “without referrer” for Facebook — real people from the in-app browser land on the White Page: “Low-trust referrer” (STRICT_TRUST_REFERRER_LOW)
What you'll see in the log when a check fires:
- cloaking off: “Cloaking switched off” (
CLOAK_OFF); - IP blacklists: “Previously flagged address” (
BLACK_IP); - VPN, proxies and datacenters: “High-risk network” (
STRICT_TRUST_NETWORK_RISK); - IPv6: “IPv6 traffic blocked” (
IPV6_BLOCKED); - no ISP: “Untrusted ISP” (
STRICT_TRUST_ISP_LOW); - no referrer: “Low-trust referrer” (
STRICT_TRUST_REFERRER_LOW); - headless browsers: “Headless browser detected” (
HEADLESS_HARD_BLOCK) if the toggle is on; “Automated browser traffic” (HEADLESS_BROWSER_TRAFFIC) if traces of automation are proven; “Automation risk detected” (STRICT_TRUST_HEADLESS_RISK) from the trust score; - require JS: “JavaScript required” (
JS_REQUIRED); - trust score below the threshold: “Trust score too low” (
STRICT_TRUST_BLOCKED); - in shadow mode, instead of a cut: “Watched, not cut” (
SHADOW_MODE).
The network toggles don't cut visits on their own; they add a penalty to the trust score, and the reason in the log names the biggest of the penalties.
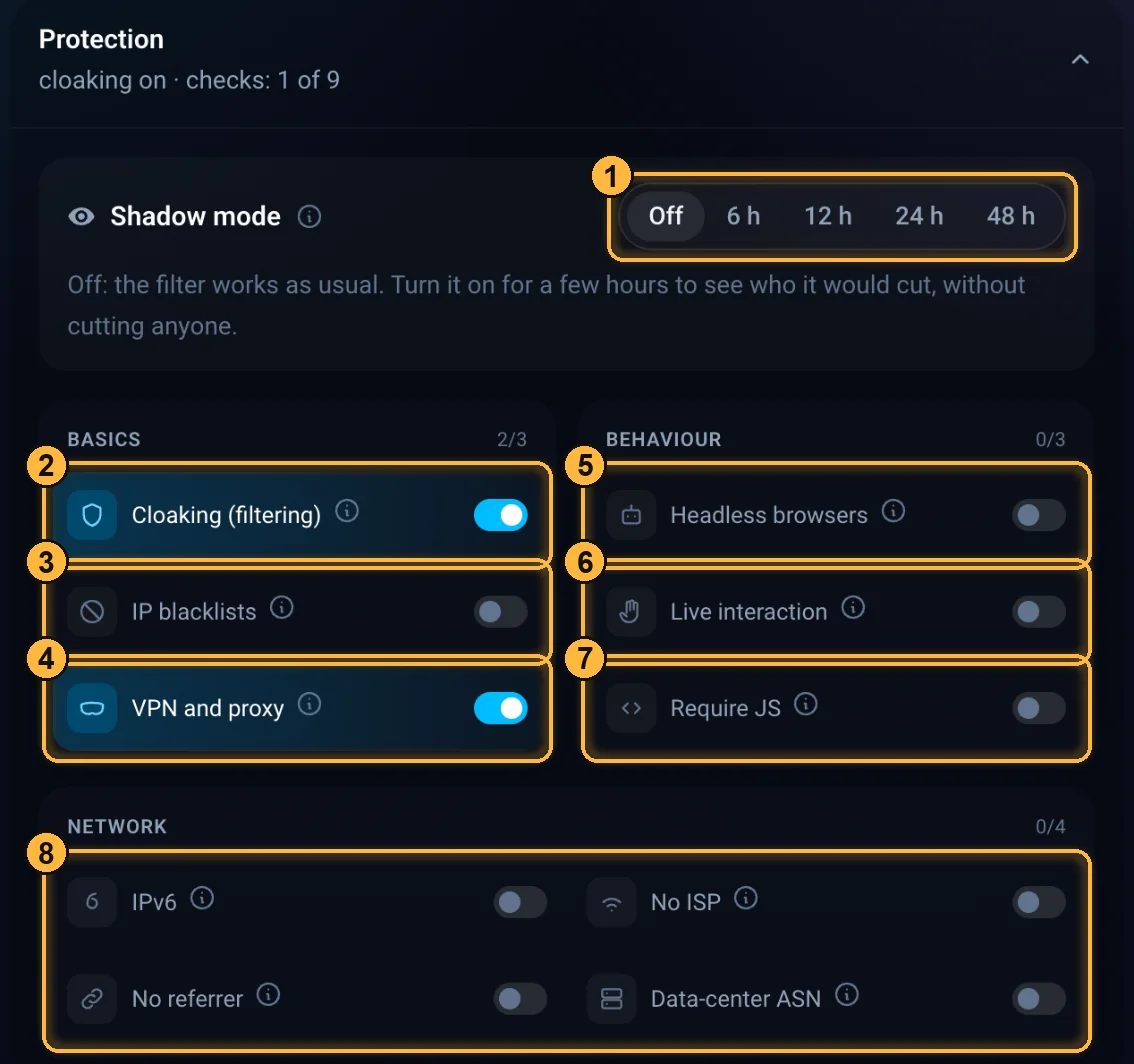
The toggles are grouped into three: “Basics”, “Behaviour” and “Network”; each group header shows how many are on. The tiles carry short names (given in brackets in the table below), and each check's description opens from the “i” icon. The block header shows a summary: “cloaking on · checks: N of 9”. Cloaking is the main toggle, with nine checks under it.
| Toggle | What it does | When to turn it on |
|---|---|---|
| Shadow mode | Buttons “Off”, “6 h”, “12 h”, “24 h”, “48 h”. The filter doesn't cut anyone, it only flags whom it would have blocked; “Diagnostics” shows whom it would have cut. It turns off on its own when time runs out; clicks in shadow mode don't use up the trial limit. Works with cloaking on and a connection via the PHP file, the Keitaro filter or Binom; when you connect with the JS tag or the link, the filter cuts as usual. The White Page is still shown to visitors of a paused or unpaid flow, addresses on your IP blacklist and all visits in review mode. While the shield is up, shadow mode has no effect. | When you suspect lost conversions or before tightening the rules. Keep it short: while it's on, the offer is open to everyone. |
| Cloaking (filtering) | The main toggle. On: every visit is checked and unwanted ones go to the White Page. Off: all visitors see the White Page. | Always on, except when you need to close the campaign for a while. |
| Block by IP blacklists (IP blacklists) | Cuts right away addresses bots have already come from, on your account or other clients'. The shared list of addresses where bots and platform reviewers have definitely been caught always applies, even with the checkbox off; only the flow's IP whitelist bypasses it. | Always. |
| Block VPN/Proxy (VPN and proxy) | Sharply lowers trust in visits through VPNs and proxies: they're used to fake the country. | When the visitor's real country matters. |
| Block IPv6 (IPv6) | Sharply lowers trust in visits from IPv6 addresses. | Only if the offer and tracker work over IPv4; otherwise you'll lose real people. |
| Block without ISP (No ISP) from Professional | Lowers trust in visits with no visible ISP; these are usually servers. | For most platforms; usually turned off for TikTok. |
| Block without Referrer (No referrer) from Professional | Lowers trust in visits where you can't see which site the visitor came from (the referrer). | Only if traffic always comes through links on the platform. Don't turn it on for Facebook. |
| Block datacenter ASN (Data-center ASN) | Lowers trust in visits from hosting and cloud networks, where scanners and bots come from. | “Balanced” and “Strict” levels. |
| Block headless (Headless browsers) | Catches bots and auto-clickers posing as a browser. A browser with proven traces of automation is cut even with the toggle off; the toggle adds cuts based on weaker signals. | Always. |
| Live interaction check (Live interaction) | Watches how the mouse and finger move: a person behaves naturally, a bot doesn't. Adds up to half a second of waiting. With the PHP file, you need its latest version. | For strict platforms; the “Strict” level. |
| Require JS (Require JS) | A visitor without JavaScript gets a heavy penalty and lands on the waiting page. Simple bots and scrapers trip on this. | When the platform passes a click tag and almost all traffic comes from regular browsers. |
Audience
- Default
- no restrictions
- Recommended
- target countries only, in “Only these” mode
- Plan
- countries, devices, OS and browsers on all plans; languages, time zones, cities, regions, networks (ASN), ISPs and referrers on Professional and up, and on the trial
- Common mistake
- opening the link from outside the target country and deciding the filter is broken: the log shows “Country not allowed” (
COUNTRY_NOT_ALLOWED); “Except these” with every country selected: “All countries blocked” (COUNTRY_DENIED_ALL)
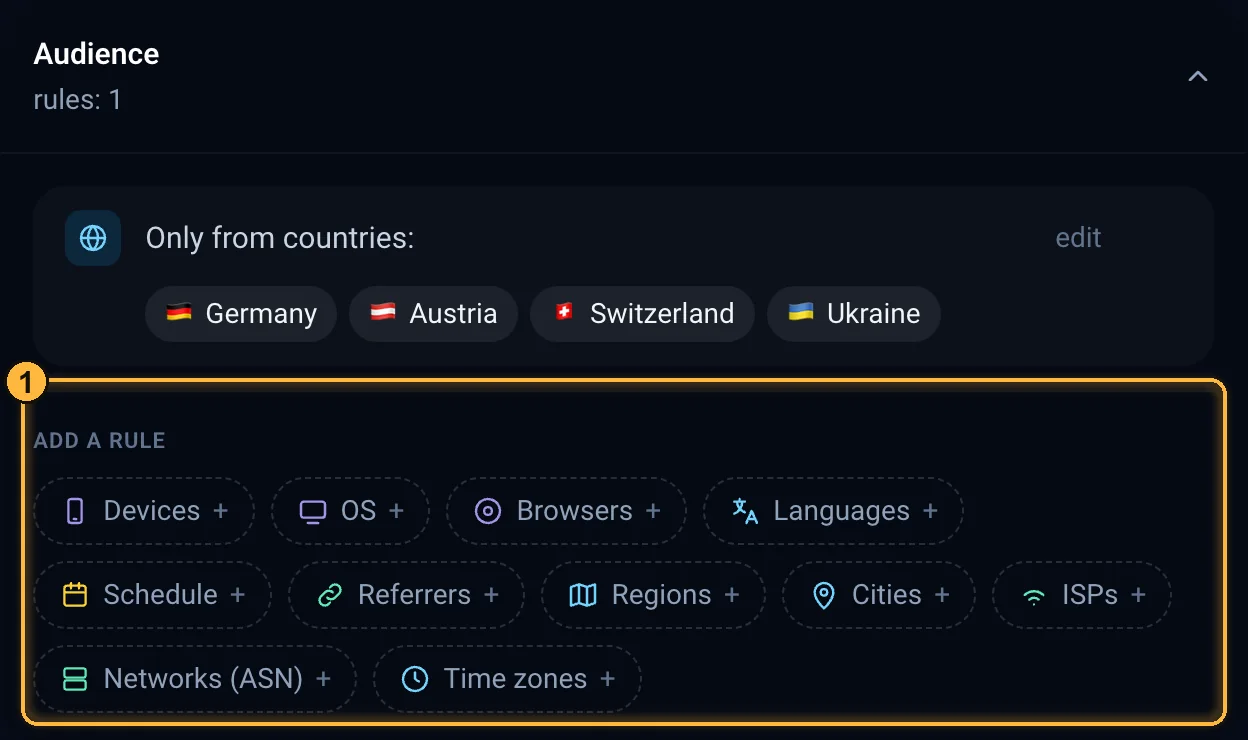
The block is collapsed, and its header shows “rules: N” or “no restrictions”. Rules you've set are shown at the top as phrases, for example “Only from countries: …” or “Not from devices: …”; click a rule to change it. A new rule is added with the buttons below them, in the Add a rule row: Countries, Devices, Schedule and others. When editing a rule, choose:
- Only these: let through only what's listed;
- Except these: let through everyone except what's listed;
- a rule with no values restricts nothing; Remove rule deletes it entirely.
A visitor who doesn't match the rule sees the White Page with a reason like “Country not allowed”.
| List | How to fill it in |
|---|---|
| Countries (GEO) | Pick from a searchable list; you can paste a comma-separated list of codes into the search, for example “ua, kz, de”. “Select all” (or “Select found”), “Clear” and “Done” buttons. |
| Devices | Mobile, Desktop, Tablet, Smart TV, Game console, Wearable, Bot / crawler, Unknown. |
| Operating Systems, Browsers | Pick from a searchable list. |
| Languages, Timezones from Professional | Pick from a searchable list. The old and new names of a time zone count as one zone: Europe/Kiev and Europe/Kyiv, Asia/Calcutta and Asia/Kolkata, Asia/Saigon and Asia/Ho_Chi_Minh; browsers often send the old one. |
| Cities from Professional | Enter names as they appear in the click log, for example “Berlin”. A value is added with Enter or a comma. |
| Regions from Professional | Region name or ISO code, for example “Bavaria” or “BY”. |
| Networks (ASN) from Professional | Network number: “AS15169” or “15169”. |
| Providers from Professional | The name as in the click log, for example “Deutsche Telekom AG”. |
| Referrers from Professional | The referring site's domain, for example “facebook.com”. Subdomains are included automatically. |
Ad schedule from Professional
- Default
- off; when you turn it on, weekdays 09:00–18:00 in your time zone are filled in
- Recommended
- the time zone of the country where the ads run
- Plan
- Professional and up, and on the trial
- Common mistake
- keeping your own time zone while the ads run in another country — the hours shift, and during business hours visits get “Outside campaign hours” (
OUTSIDE_SCHEDULE)
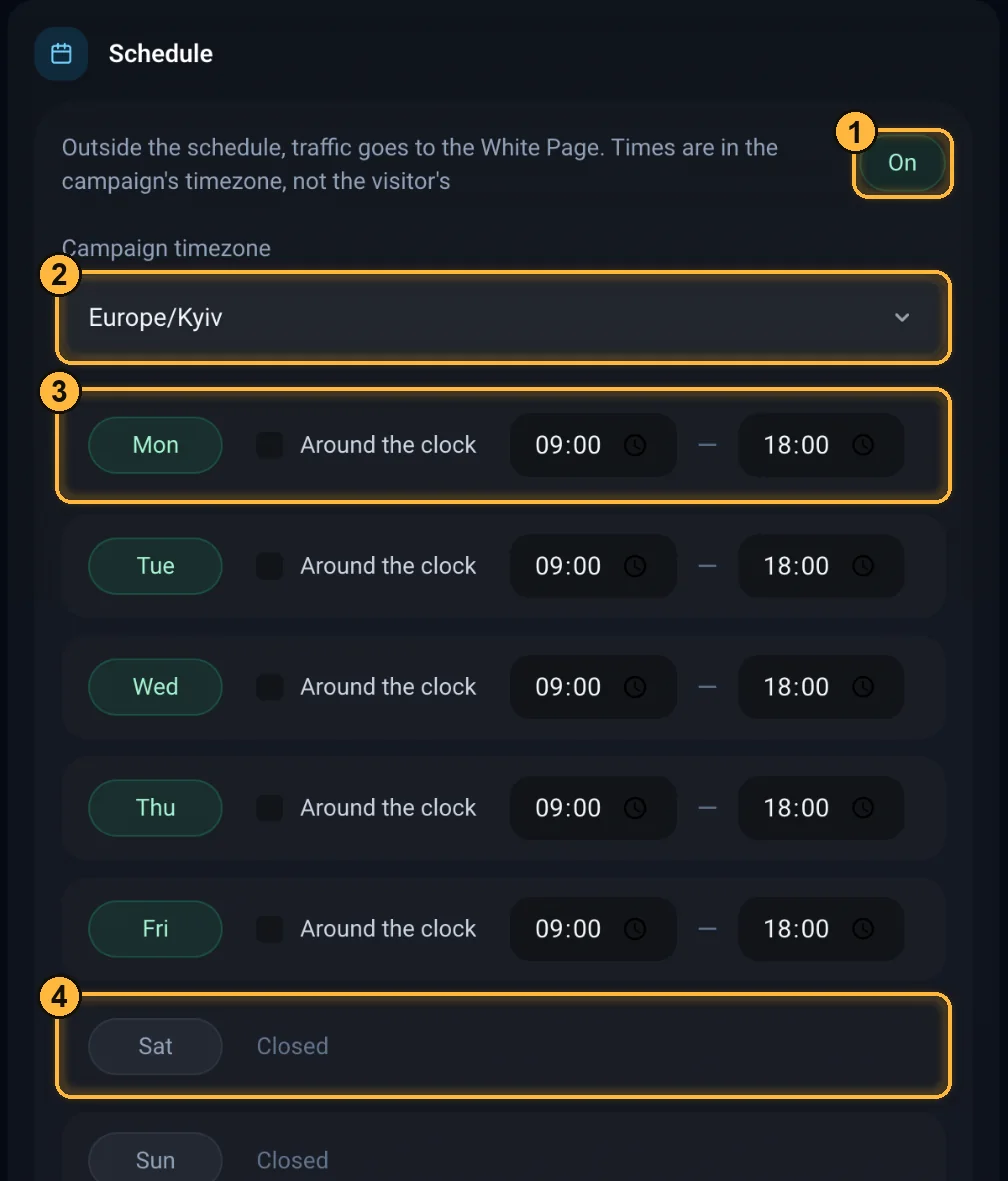
Added in the “Audience” block with the Schedule button in the “Add a rule” row; in the rule list it reads “The offer is shown on a schedule”. Outside the schedule, a visit gets “Outside campaign hours” (OUTSIDE_SCHEDULE).
- An On / Off toggle (off by default). When you turn it on, weekdays from 09:00 to 18:00 in your time zone are filled in right away.
- Campaign timezone: time is counted in it, not in the visitor's time zone.
- For each day: on or off, the Around the clock checkbox, or “from” and “to” times.
- Outside the schedule, all visitors see the White Page.
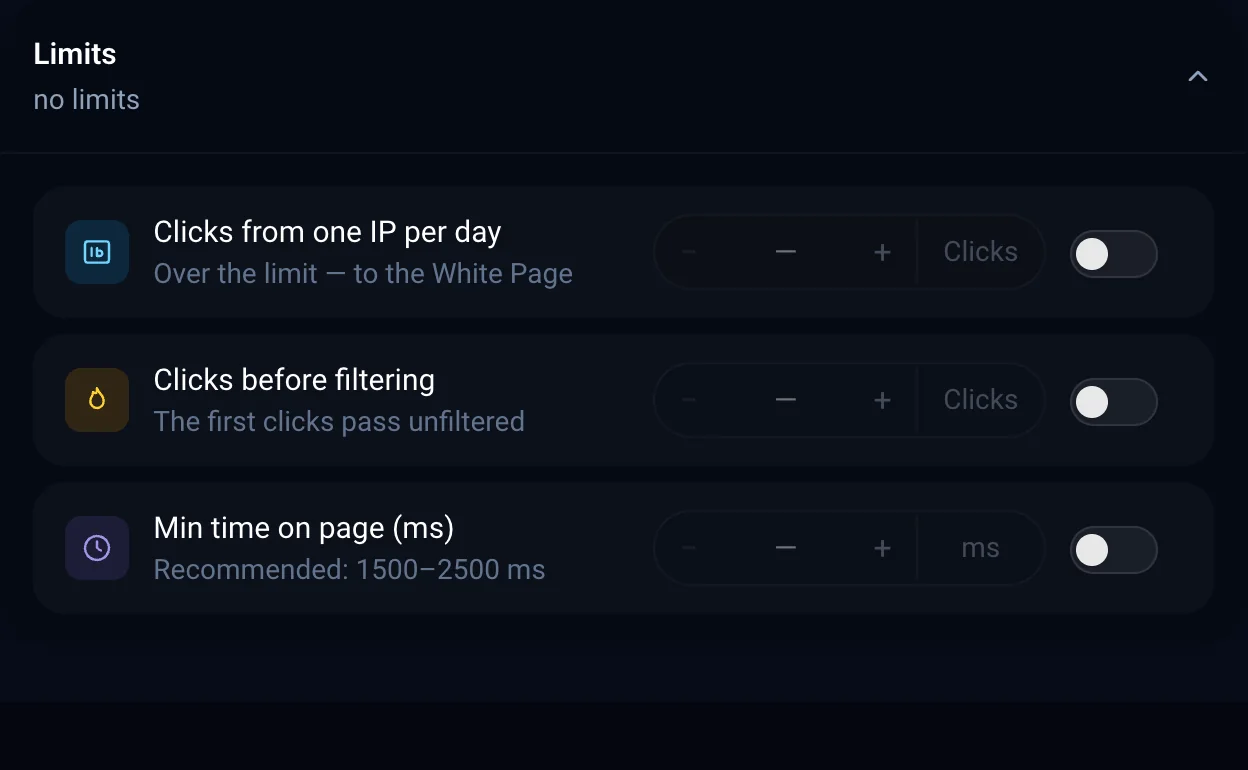
Limits
- Default
- a new flow gets the “Another source + Balanced” profile: 3 clicks per IP per day, warm-up and minimum time off; on Starter the plan switches the IP limit off
- Recommended
- per platform: 2–5 clicks per IP per day, a warm-up of 30–100 clicks
- Plan
- the IP limit and warm-up on Professional and up, and on the trial; minimum time on page on all plans
- Common mistake
- a limit that's too tight cuts your own people: “Too many clicks from one IP” (
CLICKS_PER_IP_LIMIT); everyone sees the White Page in the first hours: warm-up is in progress, “Before filtering” (BEFORE_FILTERING); visitors who leave the waiting page before the minimum don't get into the log at all
| Field | What it does | Values |
|---|---|---|
| Clicks from one IP per day from Professional | After N clicks a day from one address, the next ones see the White Page. Every visit counts, including reloads that the log merges into one click. Addresses on the IP whitelist skip this check. | 0 means no limit, up to 1,000,000 |
| Clicks before filtering (warm-up) from Professional | The flow's first N visitors see the White Page without a check: they usually include the first moderation checks. | 0 means no warm-up, up to 1,000,000 |
| Minimum time on page (ms) | A visitor who stayed less lands on the waiting page and goes through the check again. | 0 means no waiting; we recommend 1500–2500 |
ArtisanClo · Dashboard documentation. Questions — info@artisanclo.com or @artisanclo_support on Telegram.